TypeScript aliases
Follows paths, baseUrl, local configuration inheritance, and modern .mts and .cts module entry points.
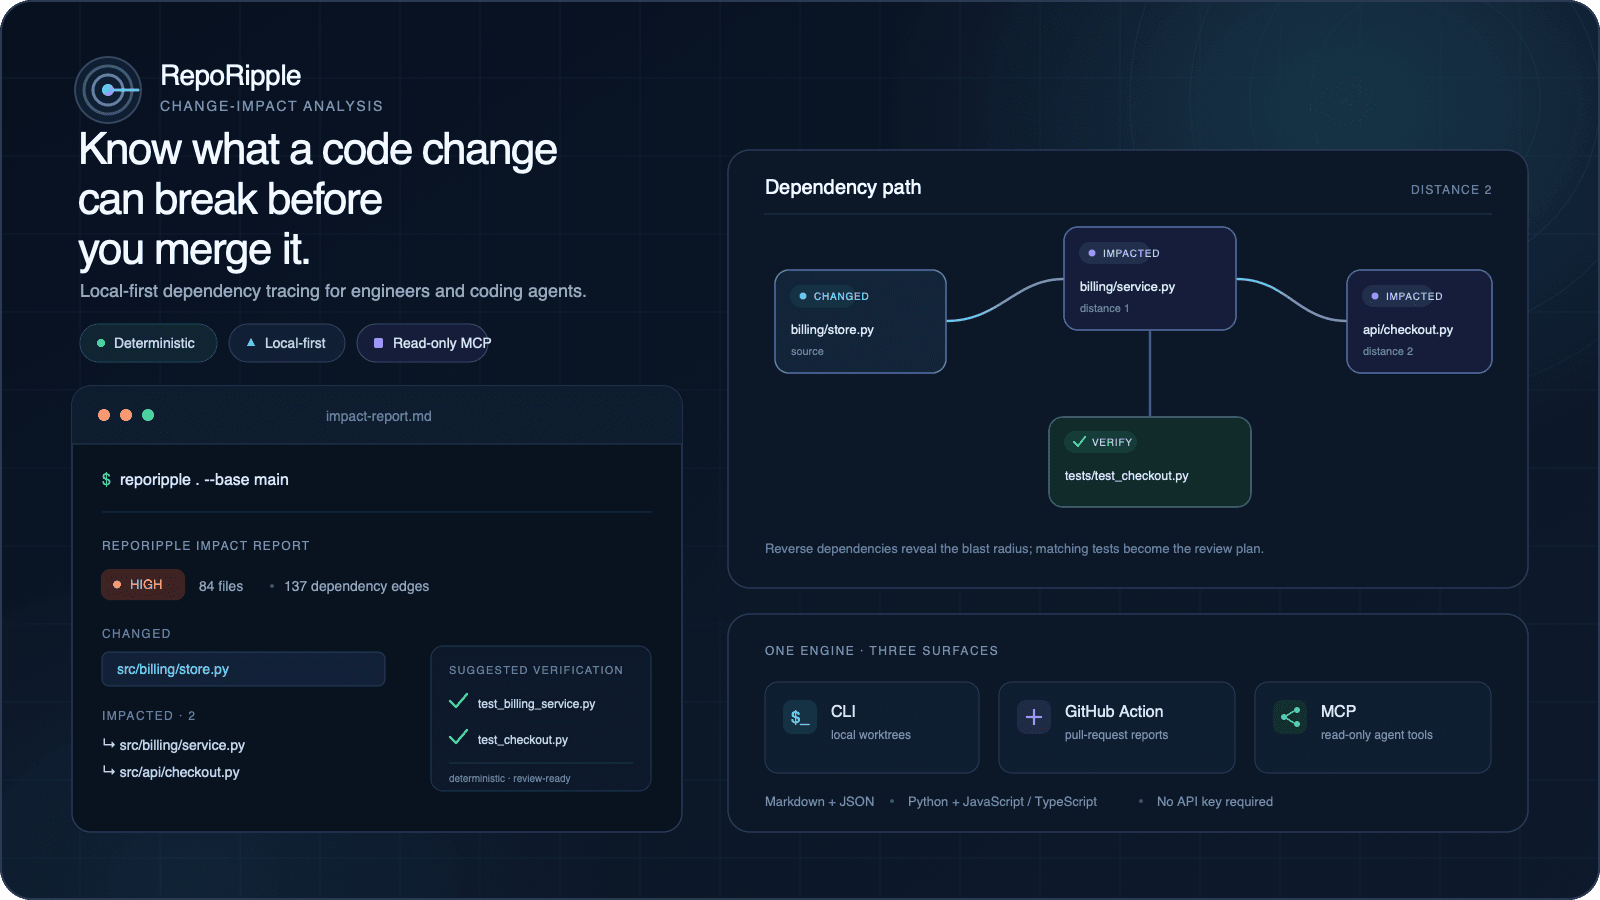
RepoRipple follows a Git change through Python imports, TypeScript aliases, and local workspace packages. It traces the blast radius, recommends relevant tests, and packages the evidence for humans and coding agents.
Published Nov 3, 2026 · Verified on Python 3.11, 3.12, and 3.13
Follows paths, baseUrl, local configuration inheritance, and modern .mts and .cts module entry points.
Connects npm and Yarn workspace imports through package entry points, subpath exports, and conditional exports.
Retains pre-change dependency evidence so deleted and renamed source files still reveal their remaining dependents.
Workspace support reads local package.json declarations. External packages and pnpm-workspace.yaml are not resolved; configuration-only changes are flagged as risk without claiming a complete importer map.
Analyze a worktree or compare a branch, then emit a review-ready Markdown or JSON report.
Attach impact evidence to pull requests and fail CI when a change crosses a configured risk threshold.
Give coding agents typed tools to forecast proposed edits or inspect real changes inside an allowed workspace root.
The deterministic path needs no API key or hosted service. Use the package directly, run it without installing through uvx, or start its local MCP server.
pip install reporipple
reporipple . --base origin/main

# No-install execution
uvx reporipple . --base origin/main

# Read-only MCP server
uvx reporipple mcp --root /path/to/workspacePublished on PyPI and in the MCP Registry.